Security & Deployment
Security, compliance
& deployment
NeuroGlass runs where your data already lives — your cloud or on-prem, your storage, your access controls. Built to pass enterprise security review and deploy inside your own validated, compliant environment.
Trusted by teams at



Your data never moves
Point NeuroGlass at your existing private S3 buckets and stream terabyte-scale volumes straight into the browser — no copies, no migration, nothing leaving your control. NeuroGlass mediates access under your permissions; you keep ownership and can revoke or delete at any time.
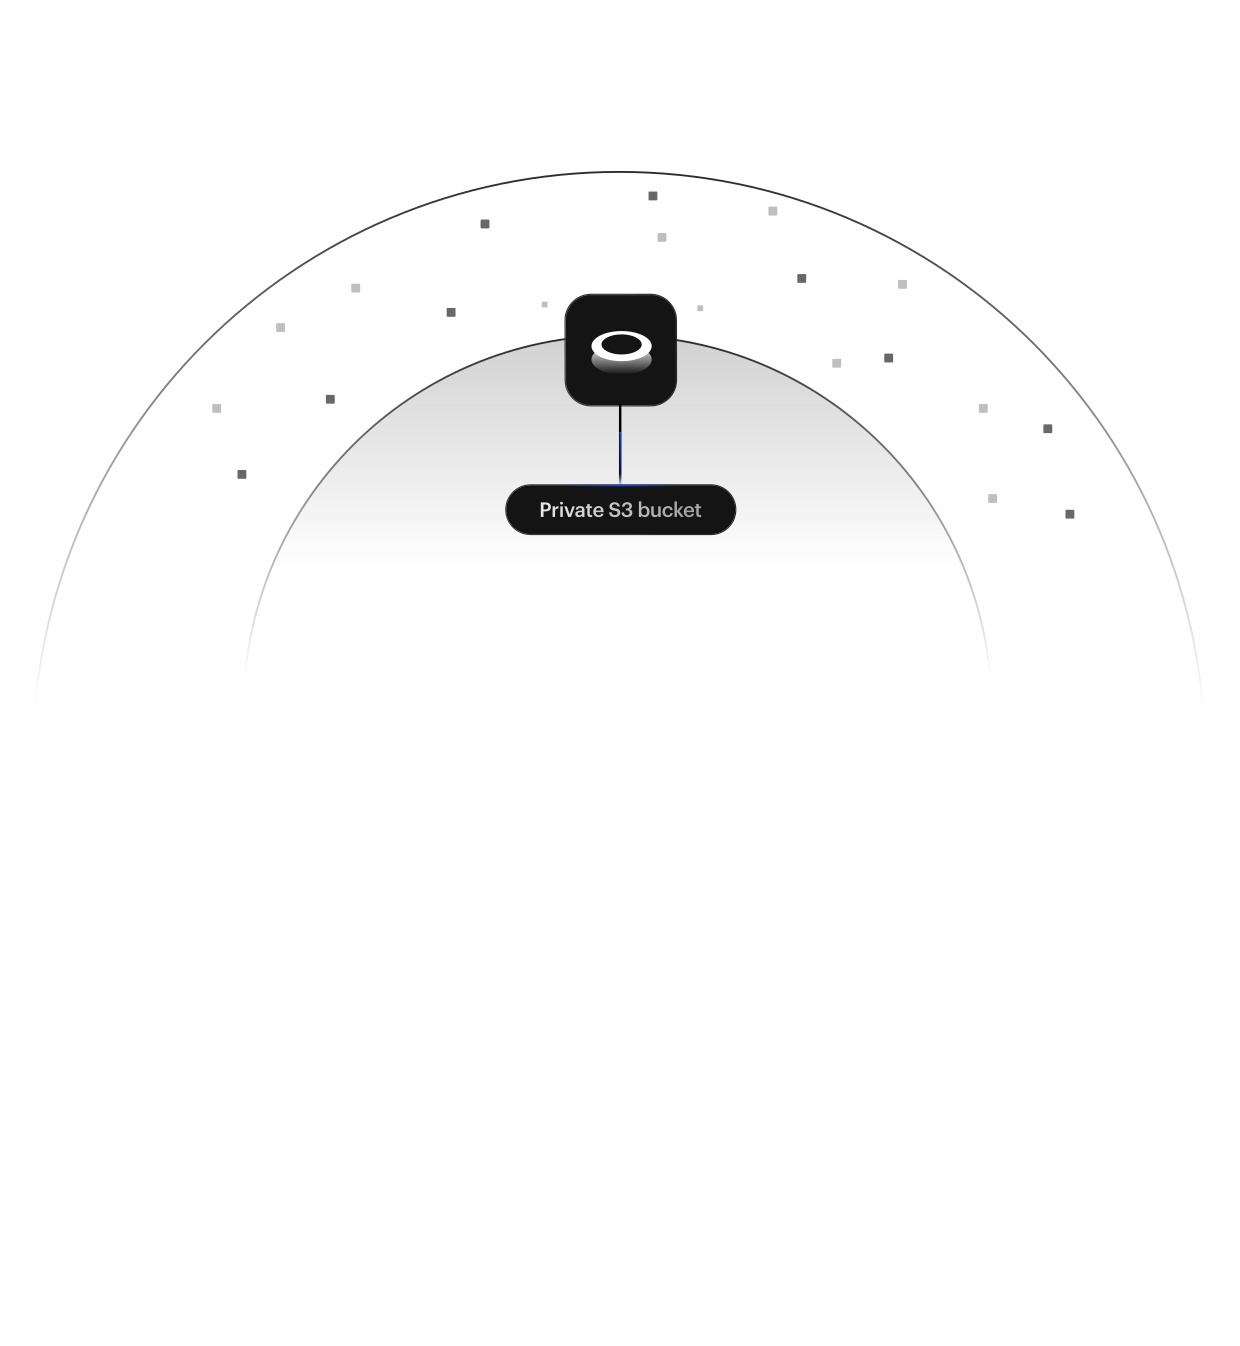
Secure. Controlled. Yours.
Controls that survive procurement
Single sign-on, granular access, and deployment that keeps data in your own environment and region — the controls an enterprise security review asks for.
Single sign-on & role-based access
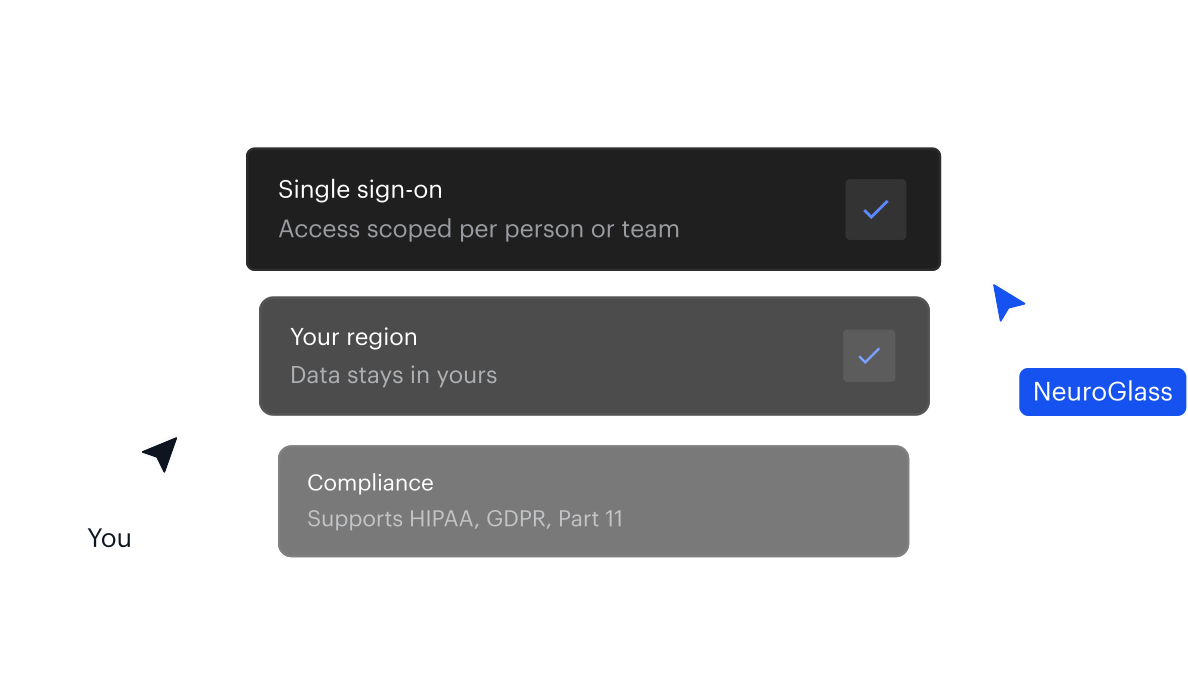
SSO and Google-Docs-style permissions via Keycloak. Grant, scope and revoke access per person, team or dataset across your organization.
Your storage, your region
Data stays in your own buckets, account and region — including EU residency through MetaCell S.r.l. NeuroGlass connects over encrypted channels and never duplicates your datasets.
Built for your compliance environment
Deploy in a way that supports your regulatory requirements — HIPAA, GDPR and 21 CFR Part 11 — inside your own validated, controlled environment.
SaaS or on-prem — your infrastructure
Deployment that fits your infrastructure
Run it as managed SaaS, or deploy on-prem in Kubernetes on your own cloud — no external cloud dependencies.
for your security review
What your reviewers can ask us for
Reach out to us, and we'll answer in writing or walk through it with your team.
Your security questionnaire, answered
Send us your organization's questionnaire and we'll answer it for the deployment you're evaluating: our cloud, your own cloud or on-prem.
An architecture and data-flow walkthrough
An engineer shows your team where the data lives, how it streams to the browser, what NeuroGlass stores, and how single sign-on and permissions work.
no lock-in
Nothing to be locked into
NeuroGlass is built around open Neuroglancer. Your views are portable Neuroglancer JSON and your data stays in open formats in your own storage — so you can walk away with everything, any time.
Portable by design
Every view is standard Neuroglancer state — copy it, version it, or open it elsewhere. No proprietary project format holding your work hostage.
Open formats, your storage
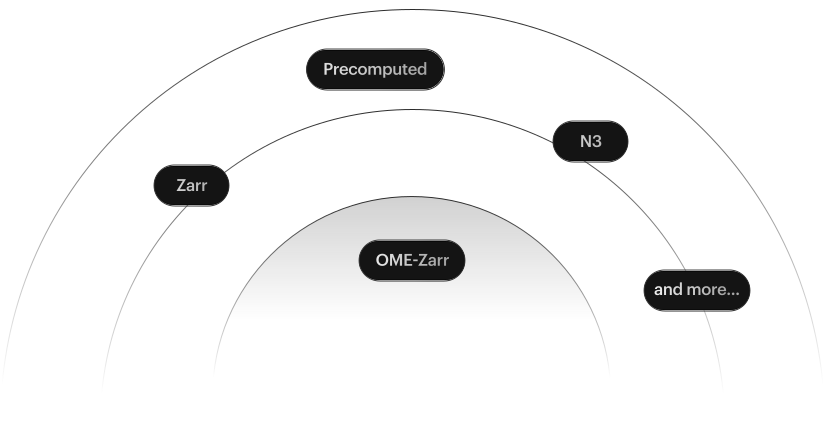
OME-Zarr, Zarr, N5, Precomputed and more, streamed from your own buckets. Stop paying NeuroGlass tomorrow and your data is still exactly where it always was.
Bring us your security review
Send us your questionnaire, or walk through a deployment in your own environment with one of our engineers. We'll map NeuroGlass to your controls, region and compliance requirements.
Frequently Asked Questions
Can't find an answer? Contact us
Where does our data actually live?
Can we deploy on-prem, with no external cloud dependencies?
How does access control work?
Does NeuroGlass support HIPAA, GDPR and 21 CFR Part 11?
What happens to our work if we stop using NeuroGlass?
Allen Institute using NeuroGlass to support large-scale brain imaging workflows
Read the Press Release


